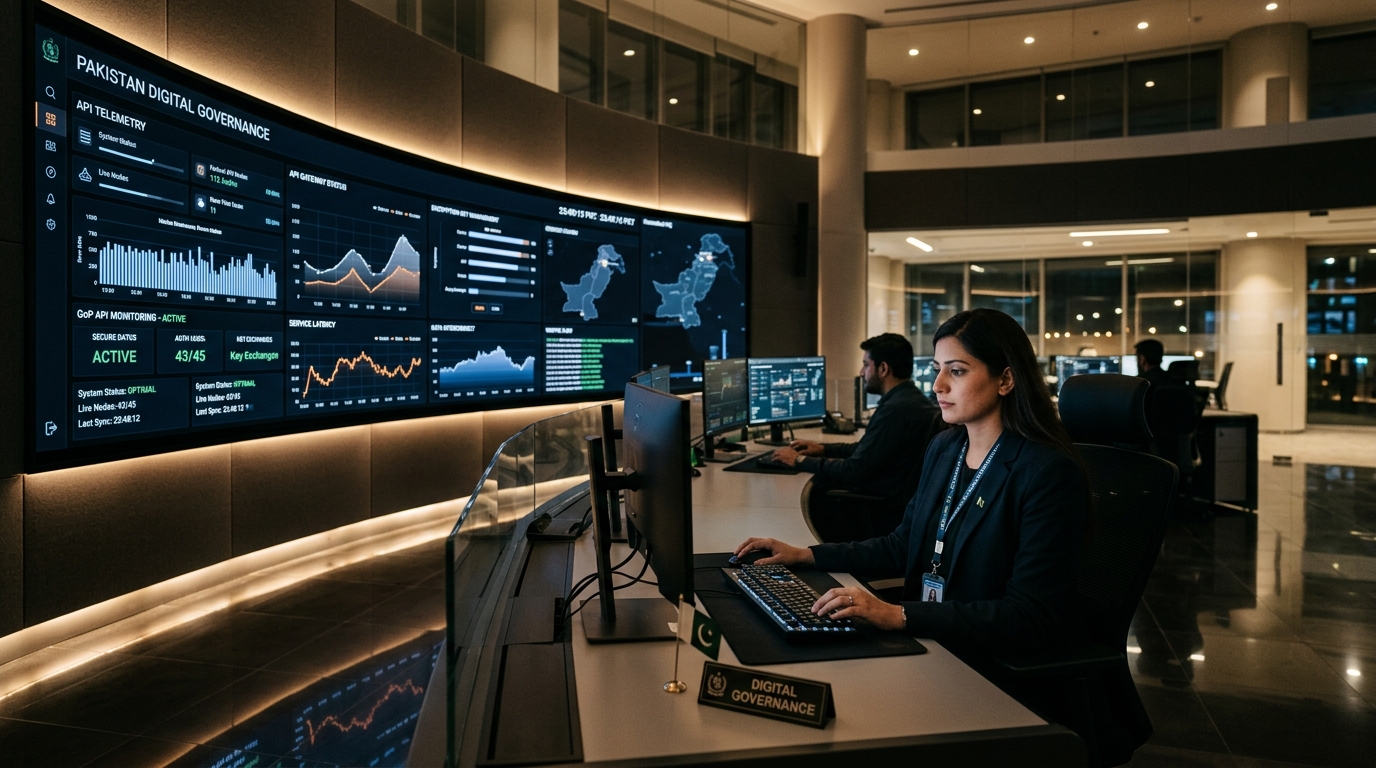
In a structural leap forward for sovereign digital governance, the Ministry of Information Technology and Telecommunication (MoITT), in technical collaboration with the National Information Technology Board (NITB), has officially operationalized the National Data Exchange Layer (NDEL).
Modeled on Estonia’s globally acclaimed X-Road distributed digital architecture, NDEL establishes a secure, zero-trust cryptographic service bus that interconnects Pakistan’s primary federal databases, provincial administrative departments, regulated banking switches, and licensed FinTech ecosystems. By replacing fragmented, brittle point-to-point integrations with a standardized sovereign API fabric, NDEL unlocks automated, paperless inter-agency workflows while strictly preserving distributed data ownership and citizen privacy.
The Legacy Challenge: Fragmented Data Silos and Bespoke Integrations
Before the launch of NDEL, Pakistan’s public administration and commercial banking sectors grappled with deeply entrenched architectural fragmentation. Over decades, key state authorities developed independent, siloed database systems:
- NADRA (National Database and Registration Authority): Maintained sovereign citizen identity, family registration, and biometric ledgers.
- FBR (Federal Board of Revenue): Operated tax filer returns, wealth statements, withholding records, and Sales Tax Registration Number (STRN) registries.
- SECP (Securities and Exchange Commission of Pakistan): Governed corporate registry records, director filings, and statutory compliance data.
- State Bank of Pakistan (SBP) & Interbank Rails: Supervised high-value clearing (PRISM), the 1LINK national switch, and the Raast instant payment system.
- Provincial Land Revenue & Excise Authorities: Managed localized cadastral registers, real estate titles, and motor vehicle registrations across disparate provincial software stacks.
flowchart LR
    subgraph Legacy_Architecture["Legacy Point-to-Point Architecture (Pre-NDEL)"]
        direction TB
        B1["SECP"] <-->|"Bespoke Custom API"| B2["FBR"]
        B2 <-->|"Manual SFTP Batches"| B3["NADRA"]
        B3 <-->|"Paper Attestation"| B4["Banks"]
        B4 <-->|"Physical Visits"| B5["Land Revenue"]
        B1 <-->|"Bespoke Custom API"| B4
    end

    subgraph NDEL_Architecture["NDEL Sovereign Interconnect Fabric (Current)"]
        direction TB
        N1["SECP Security Server"] <--> BUS(("NDEL Sovereign Mesh Bus"))
        N2["FBR Security Server"] <--> BUS
        N3["NADRA Security Server"] <--> BUS
        N4["Banking Rails Security Server"] <--> BUS
        N5["Provincial Land Registry"] <--> BUS
    end
Under this legacy framework, validating citizen or enterprise credentials across departmental boundaries required manual physical visits, notarized paper attestations, or custom-built, bilateral point-to-point APIs. These point-to-point connections proved brittle, insecure, and operationally unsustainable:
- Proliferation of Custom Integrations: Every new cross-agency data exchange required a proprietary API, custom network tunnels, and disparate authentication rules, multiplying development cycles and operational overhead.
- Synchronization Lags and Inconsistencies: Batch file transfers over SFTP or scheduled database synchronization created information lags of 24 to 72 hours, resulting in fraudulent tax claims, ghost company registrations, and delayed credit underwriting.
- Security Vulnerabilities: Bilateral integrations lacked centralized cryptographic attestation, mutual non-repudiation, and standardized audit logging, complicating forensic investigations during security incidents.
NDEL eliminates this architectural debt by introducing an encrypted, decentralized service bus that standardizes cross-agency data exchange under a unified national standard.
NDEL Distributed Architecture: Sovereign Zero-Trust Service Bus
Architecturally inspired by the Nordic and Estonian distributed e-governance paradigms, NDEL strictly rejects the concept of a monolithic central database. Creating a single centralized repository of all citizen and enterprise information would create an unacceptable national security risk and an irresistible target for state-sponsored cyber adversaries.
Instead, NDEL functions as a decentralized, peer-to-peer data interchange grid where data remains permanently at rest within the custodian institution’s primary systems.
flowchart TD
    subgraph Agency_A["Consuming Agency (e.g., Commercial Bank / SECP)"]
        APP_A["Client Business Application"] --> ADAPT_A["Local API Adapter"]
        ADAPT_A --> SS_A["NDEL Security Server A"]
        SS_A --> HSM_A["Sovereign HSM (mTLS & Payload Signing)"]
    end

    subgraph Central_Services["NDEL Central Governance Infrastructure (NITB)"]
        CENTRAL_REG["Global Central Registry (PKI Directory)"]
        TSA["RFC 3161 Distributed Time-Stamping Authority"]
        MONITOR["Cryptographic Telemetry & Health Monitor"]
    end

    subgraph Agency_B["Provider Agency (e.g., FBR / NADRA / Land Revenue)"]
        SS_B["NDEL Security Server B"]
        HSM_B["Sovereign HSM (Decryption & Verification)"]
        SS_B --> HSM_B
        SS_B --> ADAPT_B["Service API Adapter"]
        ADAPT_B --> DB_B[("Sovereign Custodian Database")]
    end

    SS_A <-->|"Fetch Directory & Revocation Lists"| CENTRAL_REG
    SS_A <-->|"RFC 3161 Timestamp Token"| TSA
    SS_A <==|"Mutual TLS 1.3 / Enveloped Signed Payload"|==> SS_B
Core Architectural Pillars
- Decentralized Security Servers: Every participating public body, regulated bank, or licensed enterprise operates an accredited NDEL Security Server at the edge of their sovereign network perimeter. The Security Server manages mutual TLS (mTLS) handshake validation, certificate revocation verification (via OCSP stapling), payload encryption, and digital signatures.
- Hardware Security Module (HSM) Integration: All cryptographic operations—including transaction signing and decryption—are executed within FIPS 140-2/3 Level 3 validated Hardware Security Modules deployed locally. Encryption keys never exist in plaintext memory on host operating systems.
- Mutual Non-Repudiation and Time-Stamping: Every request and response payload transmitted across NDEL is stamped by an RFC 3161-compliant sovereign Time-Stamping Authority (TSA) and cryptographically signed. The resulting cryptographic audit trail provides indisputable legal proof of who accessed which record, when, and for what statutory purpose.
- Decentralized Registry Governance: NITB maintains the central registry that manages public key infrastructure (PKI) certificates, service catalogs, and role-based access control policies. However, no payload data ever traverses the central registry; application traffic flows directly point-to-point between the respective Security Servers across sovereign domestic networks.
Real-World Applications: Digital Governance and FinTech Transformation
The operationalization of NDEL transforms routine administrative processes from multi-week bureaucratic marathons into instantaneous, sub-second API transactions.
sequenceDiagram
    autonumber
    actor Founder as Business Founder
    participant SECP as SECP Digital Portal
    participant NDEL as NDEL Security Bus
    participant NADRA as NADRA Identity Rail
    participant FBR as FBR IRIS Engine
    participant Bank as Commercial Bank Rail

    Founder->>SECP: Submits Digital Incorporation Filing
    SECP->>NDEL: Dispatches Multi-Agency Interconnect Query
    NDEL->>NADRA: Live Biometric e-KYC Verification
    NADRA-->>NDEL: Cryptographic Identity Assertion (Verified)
    NDEL->>FBR: Request Automated NTN & STRN Issuance
    FBR-->>NDEL: Generated NTN & Sales Tax Credentials
    NDEL->>Bank: Automated Corporate Account Opening Payload
    Bank-->>NDEL: IBAN Provisioned & Linked
    NDEL-->>SECP: Consolidated Multi-Agency Settlement
    SECP-->>Founder: Complete Digital Incorporation in Under 15 Minutes
1. 15-Minute Paperless Business Incorporation
Through the synchronized integration of SECP, FBR, and commercial banking rails via NDEL, entrepreneurs can incorporate a company, obtain a National Tax Number (NTN) and Sales Tax Registration (STRN), and open a fully functional corporate bank account in under 15 minutes. The founder inputs their credentials once; NDEL orchestrates the cryptographic validation across NADRA for biometric identity verification, registers the corporate entity with SECP, generates tax identifiers from FBR’s IRIS system, and transmits pre-verified KYC tokens to the chosen commercial bank.
2. Real-Time Collateral and Credit Verification for FinTech & Banking
Under traditional loan underwriting processes, verifying collateral for micro, small, and medium enterprises (MSMEs) required weeks of physical land title inspections, manual tax return validation, and vehicle registry searches.
With NDEL, licensed commercial banks and Digital Retail Banks (DRBs) execute real-time, programmatic risk assessments:
- Land Registry Verification: Instant queries verify title ownership, encumbrances, and parcel boundaries across digitized provincial cadastral registers.
- Asset and Vehicle Verification: Real-time API calls to provincial Excise, Taxation & Narcotics Control departments confirm vehicle ownership and lien-free status.
- Tax Compliance Status: Instant checks against FBR’s Active Taxpayer List (ATL) and verified revenue brackets enable automated algorithmic working capital lines without requesting paper audited financials.
3. Targeted Social Safety Nets and Subsidies
For welfare initiatives such as the Benazir Income Support Programme (BISP) and targeted utility subsidies, NDEL facilitates dynamic, fraud-resistant eligibility scoring. Rather than relying on outdated static poverty census data, welfare disbursement engines authenticate applicants via live NADRA biometric e-KYC while cross-referencing real-time wealth proxy indicators (such as property holdings, motor vehicle assets, and utility consumption tiers) over NDEL, ensuring that public disbursements reach intended vulnerable beneficiaries.
Privacy by Design and Zero-Knowledge Verification
A critical constitutional and technical consideration embedded into NDEL’s governance framework is the principle of data minimization and zero-knowledge verification.
In legacy data-sharing setups, an institution requesting verification often received an unredacted data dump. For example, a commercial bank verifying an applicant’s income frequently requested certified copies of complete income tax returns, exposing sensitive personal expenditures, spouse assets, and medical deductions unrelated to creditworthiness.
flowchart TD
    subgraph Traditional_Data_Sharing["Legacy Data Ingestion (High Risk)"]
        BANK_OLD["Commercial Bank"] -->|"Request Complete Tax Return"| FBR_OLD["FBR IRIS Database"]
        FBR_OLD -->|"Returns Full Financial Dossier (PII Leakage)"| BANK_OLD
    end

    subgraph NDEL_ZK_Verification["NDEL Zero-Knowledge Boolean Model (Privacy-First)"]
        BANK_NEW["Commercial Bank"] -->|"Query: IsAnnualIncomeAbove(PKR 2.5M)?"| SS_IN["NDEL Ingress Node"]
        SS_IN -->|"Encrypted Assertion Request"| SS_OUT["FBR NDEL Security Server"]
        SS_OUT -->|"Local SQL Evaluation inside FBR Perimeter"| FBR_SEC[("FBR Local Database")]
        FBR_SEC -->|"Local Result: True"| SS_OUT
        SS_OUT -->|"Signed Cryptographic Token: status=TRUE"| BANK_NEW
    end
NDEL mandates Boolean and Threshold-Based Queries:
- Instead of returning a full tax return, the FBR NDEL adapter responds to a signed assertion:
verify_taxpayer_active(CNIC)oris_income_above(threshold, CNIC), returning a cryptographic boolean (TRUE/FALSE) accompanied by a digital signature. - Land revenue adapters respond to
owns_property_in_district(CNIC, District_ID)rather than dumping full cadastral records. - Vehicle registries confirm whether a specific vehicle registration number is registered under a given CNIC and whether existing bank hypothecation liens exist.
By design, data custodians never surrender ownership of raw records, and data consumers receive only the precise, minimal assertion required to fulfill a statutory or commercial transaction.
The Infrastructure Imperative: Sovereign Bare-Metal and Low-Latency Datacenters
The operationalization of NDEL introduces strict regulatory requirements regarding where and how participating institutions host their NDEL Security Servers, API adapters, and core database systems.
Under the notified National Cloud-First Policy 2.0 and the regulatory guidelines issued by the State Bank of Pakistan (SBP Framework for Cloud-Based Services) and SECP, NDEL nodes and participating workloads fall under Class-2 (Confidential PII) and Class-3 (Critical National Infrastructure) data classifications.
Why Foreign Hyperscalers Cannot Host Sovereign NDEL Workloads
- Statutory Prohibition: Public sector ministries, scheduled commercial banks, and national switches are legally prohibited from routing or storing Class-2 and Class-3 citizen data on overseas public cloud regions. Doing so violates national data residency mandates and exposes sovereign records to foreign extraterritorial discovery laws.
- Cryptographic Key Jurisdiction: NDEL requires that cryptographic signing keys reside in accredited domestic Hardware Security Modules physically located within Pakistan. Public cloud providers whose physical datacenters operate in offshore jurisdictions cannot fulfill this sovereign custody requirement.
- Deterministic Latency for High-Throughput Interconnects: Point-to-point mTLS handshakes, real-time cryptographic signature verification, and multi-agency query orchestration require predictable, single-digit millisecond latency. Routing API calls to overseas cloud regions introduces network latencies exceeding 130ms, causing timeouts during complex multi-hop transactions (such as business incorporation workflows).
flowchart LR
    subgraph Non_Compliant_Route["Offshore Public Cloud (Non-Compliant & High Latency)"]
        REQ1["Citizen NDEL Request"] -->|"Cross-Border Routing 120ms+"| TRANSIT["Subsea Cables"]
        TRANSIT --> FOREIGN_REG["Overseas Cloud Region (EU / Gulf)"]
        FOREIGN_REG -->|"Foreign Key Custody / Subject to CLOUD Act"| JURIS_RISK["Jurisdictional & Security Risk"]
    end

    subgraph Sovereign_Domestic_Route["Accredited Domestic Bare-Metal (Compliant & Ultra-Low Latency)"]
        REQ2["Citizen NDEL Request"] -->|"Sub-10ms Metro Transit"| PKIX["Pakistan Internet Exchange (PkIX)"]
        PKIX --> DEDICATED["Domestic Tier-3/Tier-4 Bare-Metal Datacenter"]
        DEDICATED --> SEC_SERVER["NDEL Security Server & Sovereign HSM"]
        SEC_SERVER --> LOCAL_DB[("Local Institutional Core Systems")]
    end
To maintain regulatory compliance and high availability, participating commercial banks, fintechs, and government line departments are deploying on robust, domestic enterprise infrastructure. Utilizing high-performance Dedicated Servers provides the dedicated compute capacity, hardware-isolated hypervisors, and physical root-of-trust necessary for high-throughput cryptographic processing.
Furthermore, procuring Dedicated Servers in Pakistan within carrier-neutral Tier-3 and Tier-4 datacenters directly connected to the Pakistan Internet Exchange (PkIX) guarantees sub-10ms domestic latency, redundant national fiber backbones, and full compliance with national data residency mandates.
Architectural Comparison: Interoperability Protocols
The table below contrasts NDEL with traditional public sector data integration approaches across critical technical metrics:
| Architectural Metric | Point-to-Point Bespoke APIs (Legacy) | Centralized Data Warehouse / Honeypot | NDEL Sovereign Service Bus (Current) |
|---|---|---|---|
| Data Architecture | Siloed, fragmented custom interfaces | Centralized master repository | Fully decentralized, federated at source |
| Security Architecture | Variable API keys, basic authentication | Perimeter defense around central store | Zero-trust, mutual TLS (mTLS 1.3), sovereign HSMs |
| Auditability & Logging | Departmental application logs (mutable) | Central database audit logs | Cryptographic, RFC 3161 timestamped, non-repudiable |
| Privacy Safeguards | Full data disclosure upon query | Central access grants broad visibility | Zero-knowledge boolean & threshold assertions |
| Failure Domain | Isolated point failures; brittle dependencies | Single point of failure & systemic catastrophic breach | Distributed resilience; node failure does not halt grid |
| Regulatory Compliance | Non-standardized; prone to leakage | Severe risk under Cloud-First Policy | 100% Compliant with SBP, SECP, and MoITT mandates |
| Latency & Overhead | Inconsistent network routes | High serialization delays | Deterministic sub-10ms over domestic PkIX links |
Next Steps for Enterprise Software Integrators and Financial Institutions
With NDEL now live, NITB and MoITT have outlined the compliance timeline for ecosystem adoption:
- Phase 1 (Active): Federal core registries—NADRA, FBR, SECP, and the Raast interbank settlement rail—operational on primary and disaster recovery (DR) security servers.
- Phase 2 (Q1–Q2 2027): Mandatory onboarding of all Digital Retail Banks (DRBs), scheduled commercial banks, and provincial land revenue automation authorities.
- Phase 3 (Q3–Q4 2027): Accredited access extended to licensed FinTechs, Electronic Money Institutions (EMIs), insurance underwriters, and healthcare telemetry exchanges.
Enterprise engineering teams preparing to interface with NDEL must ensure that their edge API adapters, NDEL Security Servers, and HSM infrastructures are deployed on certified sovereign compute clusters capable of handling high-volume encrypted payloads with zero foreign dependencies.
Related Technical Architecture & Policy Guides
- Ministry of IT Unveils Cloud-First Policy 2.0: Sovereign Data Residency Mandate for Public Sector & Financial Clouds – Full analysis of data classification tiers and domestic hosting rules.
- NADRA Launches Nishan Pakistan Biometric e-KYC API Framework for FinTechs – Technical integration guide for instant identity authentication.
- Digital Pakistan Stack and Sovereign Open API Gateway – Examination of open public digital infrastructure across Pakistan.
- SBP & SECP Mandatory Cybersecurity Audit Directives for Financial Institutions – Audit benchmarks for banking systems and sovereign security adapters.
- Layer 7 DDoS Protection & Edge Defense for Enterprise Platforms in Pakistan – Safeguarding mission-critical API gateways against volumetric attacks.
Deploy Sovereign, Low-Latency Compute for NDEL Security Servers & Enterprise APIs
Comply with Pakistan's National Cloud-First Policy 2.0 and SBP/SECP data residency mandates. Nextgen Hosting delivers high-performance bare-metal servers, sovereign private cloud enclaves, and sub-10ms domestic fiber connectivity within Tier-3 and Tier-4 carrier-neutral datacenters in Islamabad, Lahore, and Karachi.
Related News & Regulatory Updates
- Pakistan Launches National Cyber Security Incident Response Center (NCIRC)
- PTA Activates 100G PkIX Internet Exchange Mesh Across Lahore and Karachi
- SBP Raast Cross-Border Remittance & Freelancer Settlement Rail
- National Cloud Sovereignty Act: Domestic Cloud Mandates Explained
- High-Performance Dedicated Bare-Metal Servers in Pakistan