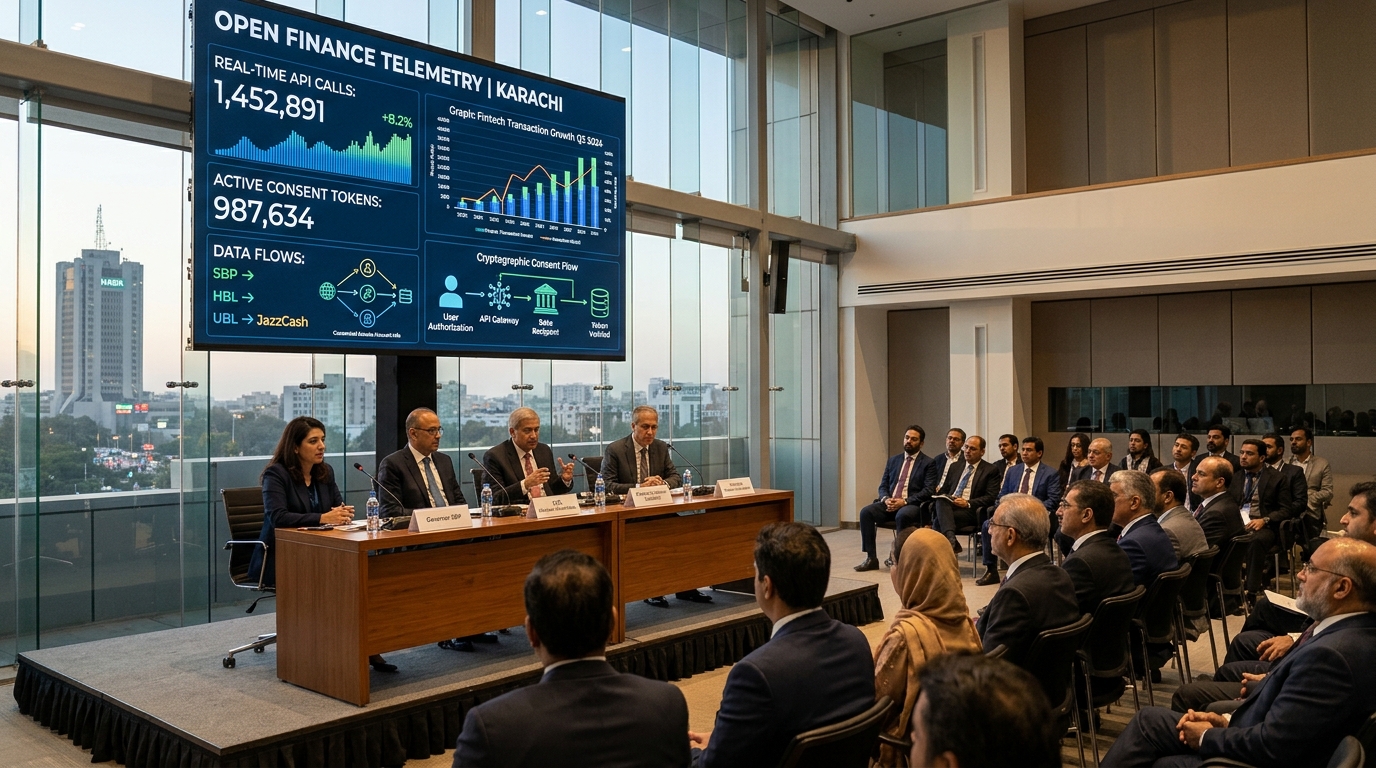
The State Bank of Pakistan (SBP) and the Securities and Exchange Commission of Pakistan (SECP) have jointly notified and operationalized the landmark National Open Finance and Account Aggregator Regulations 2026. This coordinated regulatory rollout establishes a sovereign, cryptographic Open Finance framework, dismantling decades of financial data fragmentation and introducing licensed, data-blind Account Aggregators (AAs) across Pakistan.
Under this unified architecture, Pakistani citizens, freelancers, and small-to-medium enterprises (SMEs) can securely aggregate, verify, and share their financial data in real time between commercial banks, digital retail banks (DRBs), asset management companies (AMCs), insurance providers, and brokerage houses on the Pakistan Stock Exchange (PSX). Operating under a zero-knowledge, consent-driven fiduciary mandate, the new framework provides the architectural foundation for automated algorithmic lending, instant micro-investing, and unified personal finance management.
The Financial Data Fragmentation Bottleneck in Pakistan
For decades, Pakistan’s financial ecosystem functioned within closed, proprietary institutional silos. Banking records maintained by commercial banks under SBP supervision remained entirely disconnected from capital market assets, mutual funds, and equity portfolios overseen by the SECP.
This structural partitioning imposed severe operational bottlenecks on borrowers, institutional lenders, and wealth managers:
- Bureaucratic Credit Processing Delays: Small business owners and retail borrowers applying for working capital or mortgage financing endured turnaround times ranging from three to six weeks. Financial institutions required physically attested paper bank statements, utility vouchers, stamped salary slips, and manual branch-level balance certificates.
- Freelance and Gig Economy Exclusion: Over 3 million Pakistani digital freelancers, remote engineers, and gig economy workers generating substantial foreign exchange inflows were routinely classified as “unscoreable” or high-risk. Because their earnings arrived across multi-currency fintech wallets, international remittance channels, and disparate domestic accounts, traditional credit risk models failed to capture their true debt-service capacity.
- Vulnerability to Forgery and Friction: Manual document verification was notoriously susceptible to physical document forgery, inflated balance certifications, and human processing errors, forcing risk committees to impose punitive risk premia and demand heavy real estate collateral.
- Friction in Capital Market Deepening: Opening an investment account with a PSX brokerage house or subscribing to a voluntary pension scheme required duplicative KYC submissions, even if the retail investor was already verified at Tier-2 under NADRA biometrics at a commercial bank.
The National Open Finance Framework resolves this systemic inefficiency by replacing physical document workflows with cryptographic, machine-readable data conduits governed by citizen consent.
The Account Aggregator (AA) Ecosystem Architecture
The regulatory framework establishes a three-tier architecture that clearly separates data custody, consent orchestration, and data consumption.
flowchart LR
    subgraph FIP_Layer["Financial Information Providers (FIPs)"]
        FIP1["Commercial Banks & Digital Retail Banks"]
        FIP2["Asset Management Companies & CDC"]
        FIP3["PSX Brokerages & Mutual Funds"]
        FIP4["Insurance & Takaful Operators"]
    end

    subgraph AA_Core["Licensed Account Aggregators (Consent Fiduciaries)"]
        AA1["Consent Artifact Lifecycle Engine"]
        AA2["FAPI 2.0 Security Gateway Switch"]
        AA3["Citizen Consent Mobile App / Web SDK"]
    end

    subgraph FIU_Layer["Financial Information Users (FIUs)"]
        FIU1["Digital Micro-Lenders & SME Credit Engines"]
        FIU2["Personal Wealth & PFMs"]
        FIU3["Mortgage & Auto Underwriting Platforms"]
        FIU4["Tax Compliance & Advisory Portals"]
    end

    Citizen["Citizen / SME Owner (Consent Granter)"] <-->|"Authorizes via Biometrics / PKI"| AA_Core
    FIP_Layer <-->|"Encrypted JWE Payloads via FAPI 2.0"| AA_Core
    AA_Core <-->|"Direct Point-to-Point Decryption"| FIU_Layer
The ecosystem defines three distinct institutional roles:
1. Financial Information Providers (FIPs)
FIPs are entities licensed and regulated by either SBP or SECP that hold customer financial data. They include:
- Commercial Banks, Islamic Banks, and Digital Retail Banks (DRBs)
- Central Depository Company (CDC) and PSX Brokerage Houses
- Non-Banking Finance Companies (NBFCs) and Asset Management Companies
- Life and General Insurance/Takaful Companies
- National Savings (CDNS) and Microfinance Banks
FIPs are legally mandated to expose standardized FAPI 2.0 (Financial-grade API) interfaces, enabling authorized requests to be answered with cryptographically signed financial records without human intervention.
2. Account Aggregators (AAs)
Account Aggregators are non-banking financial entities licensed under specialized joint SBP-SECP criteria. Crucially, an Account Aggregator acts purely as a consent fiduciary. It provides the interface through which an individual or corporate user reviews, approves, denies, or revokes data-sharing requests.
- Data-Blind Principle: An AA cannot view the cleartext contents of the financial payload passing through its switches.
- No Monetization or Storage: AAs are legally prohibited from caching, storing, reselling, or profiling user financial data. Their sole revenue model consists of transparent, per-transaction routing and consent lifecycle fees.
3. Financial Information Users (FIUs)
FIUs are regulated institutions that consume customer financial data to deliver a specific service requested by the customer. Examples include digital credit apps evaluating an SME for working capital, automated algorithmic robo-advisors optimizing investment portfolios, or mortgage originators verifying debt-to-income ratios.
Cryptographic Consent and Zero-Knowledge Data Flow
At the heart of the joint regulation lies an uncompromising cryptographic security standard designed to prevent data theft, unauthorized surveillance, and man-in-the-middle exploits.
Standardized FAPI 2.0 Specification
All data transmission in the Open Finance ecosystem must comply with the OpenID Foundation’s Financial-grade API (FAPI 2.0) Security Profile, paired with Mutual TLS (mTLS v1.3) and PKI-based certificate pinning.
sequenceDiagram
    autonumber
    actor Customer as Citizen / Borrower
    participant FIU as Digital Lender (FIU)
    participant AA as Account Aggregator
    participant FIP as Commercial Bank (FIP)

    Customer->>FIU: Apply for Instant SME Credit Line
    FIU->>AA: Initiate Consent Request (Scope: 6mo Cashflow, Purpose: Credit Underwrite)
    AA->>Customer: Prompt for Cryptographic Consent on Mobile App
    Customer->>AA: Authorize via NADRA Biometrics & Private Key Signature
    AA->>AA: Mint Signed JWS Consent Artifact
    AA->>FIP: Dispatch Consent Artifact via FAPI 2.0 Endpoint
    FIP->>FIP: Verify Signature against Central Directory & FIP Ledger
    FIP->>FIP: Extract Financial Records & Encrypt via FIU Public Key (JWE)
    FIP-->>AA: Forward Encrypted Ciphertext Payload
    AA-->>FIU: Route Encrypted Ciphertext (Data-Blind Pipe)
    FIU->>FIU: Decrypt with FIU HSM Private Key & Run Underwriting Models
    FIU->>Customer: Loan Approved & Disbursed via Raast Instant Switch
The Consent Artifact Lifecycle
Every transaction requires a cryptographically minted Consent Artifact represented as a JSON Web Signature (JWS). The artifact explicitly codifies:
- Purpose Code: A standardized taxonomic identifier defining the explicit purpose (e.g.,
SME_WORKING_CAPITAL_LOAN_V1). - Data Granularity: The precise attributes requested (e.g., net monthly cash inflow, average daily balance) rather than full transaction histories whenever possible.
- Data Frequency & Horizon: Whether the pull is one-time (ephemeral snapshot) or periodic (e.g., weekly balance monitoring during an active loan tenure).
- Expiry Timestamp: Deterministic termination of data access privileges.
- Revocability: The citizen retains the absolute legal right to revoke active consent at any moment through their AA mobile dashboard, triggering an automated revocation broadcast across connected FIPs and FIUs.
End-to-End JWE Payload Encryption
When the FIP receives a valid, verified consent token, it queries its internal core banking or depository systems, formats the response into standardized Open Finance JSON schemas, and encrypts the payload using JSON Web Encryption (JWE) utilizing the destination FIU’s public asymmetric key.
Because the Account Aggregator does not possess the FIU’s private key, the intermediary switch only observes randomized ciphertext. Even in the event of an adversary compromising the Account Aggregator’s routing infrastructure, no consumer balance, asset holdings, or transaction logs can be inspected or extracted.
Transformative Impact on Credit Underwriting and Financial Inclusion
The operationalization of Open Finance shifts Pakistan’s credit landscape from an outdated collateral-centric model to an automated cash-flow-based paradigm.
+----------------------------------------------------------------------------------------------------+
|                                    LEGACY VS. OPEN FINANCE PARADIGM                                |
+------------------------------------+---------------------------------------------------------------+
| Feature Dimension                  | Legacy Banking Workflows       | Open Finance (AA Framework)  |
+------------------------------------+---------------------------------------------------------------+
| Average Credit Approval Timeline   | 14 to 28 Business Days         | Under 90 Seconds             |
| Documentation Required             | Physical Stamped Bank Records  | Cryptographic Consent Token  |
| Underwriting Assessment Baseline   | Real Estate / Heavy Collateral | Real-Time Cash Flow Dynamics |
| Data Interoperability              | Closed Proprietary Silos       | Standardized FAPI 2.0 Rails  |
| Consumer Privacy Control           | Blanket Terms & Conditions     | Granular, Revocable Consents |
| Ecosystem Coverage                 | Commercial Banks Only          | Banks, CDC, PSX, AMCs, Takaful|
+------------------------------------+---------------------------------------------------------------+
1. Cash-Flow-Based Lending for 5 Million+ SMEs
Traditionally, high-growth tech startups, e-commerce retailers, and localized cottage industries could not secure bank financing because they lacked physical commercial real estate to pledge as collateral. Under Open Finance, digital lenders can evaluate an SME’s daily merchant inflows, vendor payments, and inventory turns directly across multiple merchant acquiring accounts. Algorithmic scoring models evaluate genuine cash flow velocity, enabling instant pre-approved credit lines disbursed in seconds over the Raast instant settlement rail.
2. Automated Financial Passport for Freelancers
Pakistan’s extensive freelance workforce can now construct a verified “Financial Passport.” By granting temporary consent, an independent software developer or graphic designer can aggregate multi-currency inward remittances from international fintech accounts, local digital retail bank balances, and mutual fund investments into a verified dossier, qualifying for auto financing, personal loans, and health coverage without corporate pay slips.
3. Unified Wealth Management & Capital Market Inflows
By linking the Central Depository Company (CDC), PSX mutual funds, and commercial banks through the AA layer, fintech platforms can launch unified financial health dashboards. Retail investors can view their aggregate net worth—from bank savings accounts and gold certificates to voluntary pension funds and equities—within a single, real-time interface, driving investment capital into Pakistan’s formal securities markets.
Technical Implementation: FAPI 2.0 Gateway Adapter Specification
For financial institutions integrating with the national Account Aggregator directory, maintaining compliant API gateways requires strict adherence to cryptographic standards. Below is a production-grade implementation of an FIP inbound consent verification and JWE data encryption pipeline written in Python:
"""
Open Finance FIP Consent Verification & JWE Data Dispatch Adapter
Compliant with SBP-SECP Open Finance Technical Standards (FAPI 2.0 Profile)
"""

import json
import time
from typing import Dict, Any
from jwcrypto import jwk, jws, jwe

class FIPDataGatewayAdapter:
    def __init__(self, fip_private_key_pem: str, central_directory_public_keys: Dict[str, str]):
        # Load FIP signing key (typically loaded from a Hardware Security Module)
        self.fip_signing_key = jwk.JWK.from_pem(fip_private_key_pem.encode('utf-8'))
        self.directory_keys = {
            kid: jwk.JWK.from_pem(pem.encode('utf-8'))
            for kid, pem in central_directory_public_keys.items()
        }

    def verify_consent_artifact(self, consent_jws_compact: str) -> Dict[str, Any]:
        """
        Validates the incoming JWS consent artifact against the trusted central AA directory.
        Verifies signature integrity, validity window, and purpose binding.
        """
        jws_token = jws.JWS()
        jws_token.deserialize(consent_jws_compact)

        # Extract Key ID from JWS header
        header = json.loads(jws_token.objects.get('header', '{}'))
        kid = header.get('kid')

        if kid not in self.directory_keys:
            raise PermissionError(f"Untrusted Account Aggregator key ID: {kid}")

        # Verify cryptographic signature using AA public key
        jws_token.verify(self.directory_keys[kid])
        consent_payload = json.loads(jws_token.payload.decode('utf-8'))

        # Check temporal validity
        current_time = int(time.time())
        if current_time > consent_payload.get('exp', 0):
            raise TimeoutError("Consent artifact has expired.")
        if current_time < consent_payload.get('nbf', 0):
            raise ValueError("Consent artifact is not yet active.")

        return consent_payload

    def package_encrypted_financial_data(
        self,
        fiu_public_key_pem: str,
        financial_records: Dict[str, Any],
        consent_id: str
    ) -> str:
        """
        Encrypts citizen financial records using the destination FIU's public key (JWE).
        Ensures zero-knowledge transit across the Account Aggregator conduit.
        """
        fiu_public_key = jwk.JWK.from_pem(fiu_public_key_pem.encode('utf-8'))

        payload_data = {
            "consent_id": consent_id,
            "timestamp": int(time.time()),
            "schema_version": "2026-FIP-RECORDS-V2",
            "data": financial_records
        }

        # Prepare JWE headers with authenticated metadata
        protected_header = {
            "alg": "ECDH-ES+A256KW",
            "enc": "A256GCM",
            "cty": "JWT",
            "kid": fiu_public_key.key_id
        }

        jwe_token = jwe.JWE(
            plaintext=json.dumps(payload_data).encode('utf-8'),
            protected=protected_header
        )
        jwe_token.add_recipient(fiu_public_key)

        # Generate compact serialized ciphertext
        return jwe_token.serialize(compact=True)
The Infrastructure Imperative: Why Open Finance Demands Domestic Bare Metal
The architectural mandates of the SBP-SECP Open Finance Framework introduce rigorous infrastructure demands that fundamentally disqualify commodity public clouds located outside Pakistan or oversubscribed virtualized hosting environments:
flowchart TD
    subgraph Non_Compliant["Prohibited Offshore / Public Multi-Tenant Cloud"]
        OC1["High Latency Jitter (120ms-180ms RTT to Singapore/Europe)"]
        OC2["No Hardware Determinism: CPU Noisy Neighbors & VM Stalls"]
        OC3["Data Sovereignty Violation: Exposes Financial Records to Foreign Subpoenas"]
    end

    subgraph Sovereign_Production["Accredited Domestic Bare-Metal Infrastructure"]
        DC1["Dedicated Hardware Security Modules (HSM) Cryptographic Offload"]
        DC2["Sub-10ms Domestic Fiber Latency to SBP, Raast, and PkIX"]
        DC3["100% SBP/SECP Class-2 Regulatory Data Sovereignty Compliance"]
        DC4["Isolated L3 Top-of-Rack Network Fabrics with DDoS Scrubbing"]
    end

    OC1 -.->|"Fails Real-Time Loan SLA"| Fail1["Disqualified"]
    OC3 -.->|"Regulatory Penalties"| Fail2["Revocation of License"]
    DC1 -->|"Approved Tier-3/Tier-4 Deployment"| Pass1["Licensed Production Operation"]
1. FAPI 2.0 Handshake Overhead & Sub-10ms Latency
Every Open Finance request initiates a chain of computationally intensive cryptographic negotiations: Mutual TLS 1.3 handshakes, ephemeral Diffie-Hellman key exchanges, HSM signature verifications, and JWE payload decryptions. If an institution attempts to route these high-frequency API calls through foreign hyperscale cloud regions in Frankfurt, Dubai, or Singapore, round-trip latency immediately climbs to 120ms–180ms.
Combined with intermediate database lookups, multi-cloud latencies compound rapidly, causing client mobile applications to experience API timeouts during live onboarding sessions. Regulated institutions deploying on high-performance Dedicated Servers and domestic Dedicated Servers in Pakistan maintain low-latency cross-connects directly to the Pakistan Internet Exchange (PkIX) and national banking fabrics, securing deterministic sub-10ms response times.
2. Strict Class-2 Data Residency & Fiduciary Compliance
The joint SBP-SECP circular explicitly designates consumer financial data, credit scores, transaction histories, and mutual fund portfolio compositions as Class-2 Financial Data. Under SBP’s Cloud Security Framework and the National Cloud Policy:
- Cleartext and cryptographic key custody must strictly reside within Pakistan’s sovereign geographic territory.
- Financial institutions are prohibited from hosting master verification keys or HSM roots of trust on offshore multitenant cloud environments subject to extraterritorial discovery laws (such as the US CLOUD Act).
- Dedicated bare-metal hardware guarantees full physical isolation, ensuring that cryptographic keys and RAM buffers are insulated from hypervisor side-channel vulnerabilities (e.g., Spectre, Meltdown, or noisy-neighbor cache leaks).
3. High-Throughput Ingestion for Digital Lending Switches
Fintech lenders running machine learning models to underwrite micro-loans must ingest, normalize, and score hundreds of JSON data points across multiple banking accounts in real time. Virtualized cloud instances frequently suffer from I/O throttling and unpredictable CPU steal times during high-volume loan application surges. Dedicated bare metal powered by high-frequency NVMe storage arrays and dedicated dual 10Gbps uplinks provides the sustained throughput required to maintain a seamless user experience.
Summary and Ecosystem Outlook
The operationalization of the joint SBP-SECP National Open Finance and Account Aggregator Regulations 2026 marks an inflection point in Pakistan’s digital economy. By transforming financial data from an institution’s private property into a consumer-owned, cryptographically portable asset, the state has built the final connective tissue between the Raast Instant Payment System, Nishan Pakistan e-KYC, and commercial capital markets.
Financial institutions, licensed fintechs, and infrastructure architects that align their engineering stacks with these standards—prioritizing FAPI 2.0 cryptographic rigor, robust zero-knowledge conduits, and sovereign domestic infrastructure—will lead Pakistan’s next wave of digital financial transformation.
Related Technical Architecture Guides
- Nishan Pakistan e-KYC API: Biometric Identity Rails for Banking & Fintech – Integrating NADRA’s contactless biometric verification gateway.
- Ministry of IT Unveils Cloud-First Policy 2.0: Sovereign Data Residency Mandates – Compliance frameworks for Class-1 through Class-3 critical cloud data.
- Fintech Cybersecurity & SBP Cloud Framework Compliance in Pakistan – Hardening core transaction switches against modern threat vectors.
- Architecting High-Throughput Redis & PostgreSQL Clusters on Bare Metal – Low-latency data caching and relational persistence for financial platforms.
Power Your Open Finance FAPI Gateway with Enterprise Bare Metal
Meet SBP and SECP data sovereignty mandates with zero compromise on performance. Nextgen Hosting delivers enterprise-grade bare-metal dedicated servers, hardware security module (HSM) hosting, and sub-10ms local network transit within accredited Tier-3 and Tier-4 datacenters in Karachi, Lahore, and Islamabad.