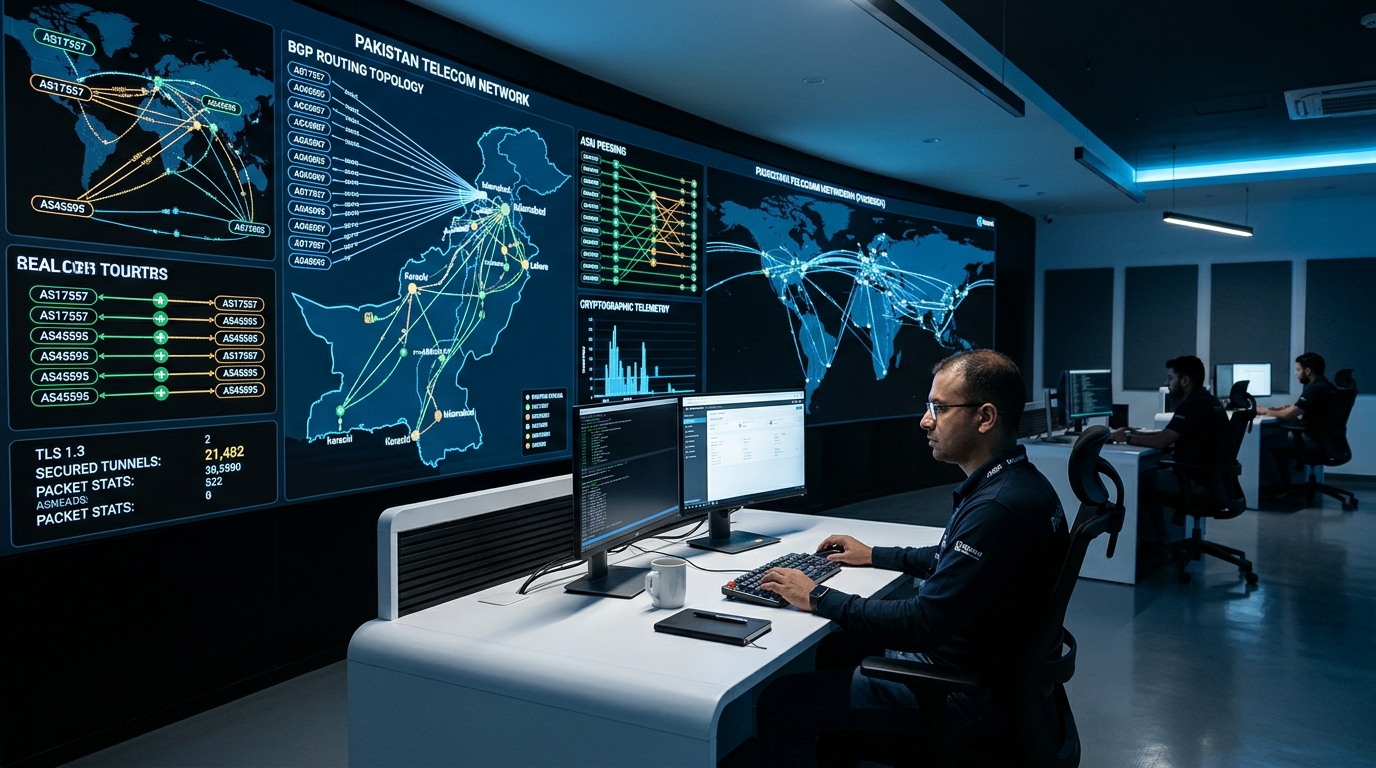
The Pakistan Telecommunication Authority (PTA), in strategic coordination with the Asia Pacific Network Information Centre (APNIC) and the Pakistan Internet Exchange (PKIX) Steering Committee, has issued the National Internet Routing Security & RPKI Enforcement Framework 2026.
The landmark regulatory mandate requires all licensed Long Distance and International (LDI) operators, Tier-1 transit telcos, cellular mobile operators (CMOs), and regional internet service providers (ISPs) operating within Pakistan to implement cryptographically verified Resource Public Key Infrastructure (RPKI) with automated Route Origin Validation (ROV). Under the strict policy directive, all Border Gateway Protocol (BGP) border routers and internet exchange switches must drop routes flagged as Invalid in real time, permanently shutting down unauthorized IP prefix hijacking, configuration-induced route leaks, and state-level traffic interception across Pakistani cyberspace.
Concurrently, the directive establishes a synchronous rollout for DNSSEC (Domain Name System Security Extensions) validation across PKNIC (the .pk country code Top-Level Domain registry), enterprise recursive resolvers, and local autonomous systems, neutralizing DNS cache poisoning and domain spoofing attacks targeting financial institutions and digital government infrastructure.
1. The BGP Security Vulnerability: Historical Routing Leaks and Prefix Hijacking
The Border Gateway Protocol (BGP)—the fundamental routing protocol that stitches together over 75,000 global Autonomous System Numbers (ASNs)—was architected in 1989 around implicit, perimeter-less institutional trust. Under standard BGPv4 routing mechanics, when an Autonomous System announces an IP prefix, adjacent peers and transit networks accept the route advertisement without cryptographic proof that the announcing ASN possesses authoritative ownership or operational delegation of that address space.
Historically, this architectural trust model has rendered Pakistani internet backbones and global routing tables vulnerable to catastrophic routing anomalies:
Accidental Route Leaks and Configuration Errors
A misconfigured internal route-map or improperly filtered internal BGP (iBGP) to external BGP (eBGP) redistribution can cause an ISP to leak localized or private prefixes onto the global routing table. In numerous high-profile global incidents over the past two decades—most notably the accidental global interception of YouTube traffic in 2008 triggered by an erroneous local sub-prefix advertisement—unauthenticated BGP announcements propagated worldwide within seconds. In Pakistan, localized routing loops have previously caused corporate and financial traffic destined for local core switches to unexpectedly egress via transcontinental undersea cables to European and Middle Eastern transits before hairpinning back into the country.
Malicious IP Prefix Hijacking and Sovereign Interception
Beyond inadvertent configuration drifts, malicious IP prefix hijacking represents an existential threat to national sovereignty. Hostile state-sponsored actors and cybercriminal syndicates utilize BGP hijacking to claim more-specific prefixes (e.g., announcing a /24 route when the legitimate owner advertises a /22 aggregate block). Under standard longest-prefix match (LPM) forwarding rules, global and domestic routers prefer the hijacked /24 announcement.
This enables adversaries to execute stealthy man-in-the-middle (MitM) inspection, traffic analysis, and cryptographic credential stripping before re-routing the traffic back to the authentic destination, leaving network operators oblivious until anomalous latency spikes or customer TLS certificate mismatches surface.
LEGACY UNAUTHENTICATED BGP ROUTING:
[Legitimate Bank / ASN 133929] ---> Announces 175.107.0.0/22 ---> Upstream Transit
                                                                       |
[Rogue / Misconfigured ASN]      ---> Announces 175.107.0.0/24 ---> Upstream Transit (Prefers /24 LPM)
                                                                       |
[Pakistani User Traffic] ---------------------------------------------> Intercepted / Blackholed!

MANDATED RPKI ROUTE ORIGIN VALIDATION (ROV):
[Legitimate Owner] ---> Publishes ROA in APNIC RPKI (ASN 133929, MaxLength /22)
                                   |
[Rogue / Misconfigured ASN] ---> Announces 175.107.0.0/24 (ASN 99999)
                                   |
[PKIX & Tier-1 Edge Routers] -> Cryptographic Check against Trust Anchor:
                                   State: INVALID (Origin Mismatch & Sub-prefix Violation)
                                   Action: AUTOMATIC ROUTE DROP (BGP Route Discarded)
2. Cryptographic Architecture: RPKI, ROAs, and Real-Time ROV Enforcement
The PTA and PKIX regulatory overhaul transitions Pakistan’s domestic and transit routing from an unverified trust paradigm to a cryptographically validated public key hierarchy backed by the Regional Internet Registry (RIR) system.
Route Origin Authorizations (ROAs)
At the foundation of RPKI is the Route Origin Authorization (ROA)—a digitally signed object formatted in CMS (Cryptographic Message Syntax) that cryptographically binds an IP address block (IPv4 or IPv6) to an authorized origin Autonomous System Number.
When an ISP or enterprise creates a ROA through APNIC’s Trust Anchor:
- The resource holder signs the ROA using their RPKI Resource Certificate, which traces its cryptographic certificate chain directly to the APNIC root Trust Anchor Locator (TAL).
- The ROA explicitly defines three parameters:
- The authoritative Origin ASN.
- The assigned IP Prefix (e.g.,
202.163.64.0/20or2400:8900::/32). - The Maximum Length (MaxLength), which designates the most specific sub-prefix that the designated ASN is permitted to announce.
Any BGP announcement from an unauthorized origin ASN, or any announcement that exceeds the specified MaxLength (such as a disaggregated /24 spawned from a /22 ROA where MaxLength was restricted to /22), is immediately classified as cryptographically Invalid.
The Route Origin Validation (ROV) Mechanics
Under PTA’s mandatory implementation guideline, Tier-1 backbones and PKIX peering fabrics deploy local RPKI Relying Party (RP) cache validators (such as Routinator, StayRTR, or OctoRPKI). These local validators continuously synchronize with global Trust Anchor repositories via the RPKI-to-Router (RTR) protocol (RFC 8210 / RFC 6810).
Border routers (Cisco IOS-XR, Juniper Junos, Nokia SR-OS, and Huawei VRP) ingest the validated cache and categorize incoming eBGP announcements into three strict evaluation states:
| RPKI Validation State | Criteria | Router Action Under PTA Directive |
|---|---|---|
| Valid | The prefix and announcing ASN precisely match an existing, cryptographically verified ROA within the permissible MaxLength. | Accepted for standard BGP path selection and local preference computation. |
| NotFound (Unknown) | No ROA covers the announced prefix in any authoritative RIR Trust Anchor database. | Temporarily accepted with normalized or reduced local preference during the national transition window. |
| Invalid | A ROA exists covering the prefix, but either the origin ASN differs from the authorized ASN, or the announced prefix is longer than the authorized MaxLength. | MANDATORY DROP: Route announcement is instantly dropped from the Routing Information Base (RIB) and never installed into the Forwarding Information Base (FIB). |
PKIX Internet Exchange Point Integration
PKIX, which maintains carrier-neutral peering nodes across Karachi (KHI01), Lahore (LHE01), and Islamabad (ISB01), has fully activated automated ROV on all route servers. Route server daemons (BIRD and OpenBGPD) automatically purge invalid announcements before redistributing routes across exchange members. This ensures that any operator peering at PKIX cannot inadvertently leak routes or hijack peer traffic across domestic cross-connects.
3. Parallel DNSSEC Mandate: End-to-End Cryptographic Domain Security
Routing security alone does not mitigate upper-layer name resolution attacks. To construct a completely hardened defense-in-depth perimeter, PTA’s 2026 circular mandates comprehensive DNSSEC (Domain Name System Security Extensions) deployment across Pakistan’s national domain registrar ecosystem, internet service providers, and sovereign digital infrastructures.
ROOT ANCHOR (.)
       |
       v  [Signed Delegation via DS Record]
.PK REGISTRY (PKNIC ccTLD)
       |
       v  [Signed Delegation via DS Record]
ENTERPRISE / BANKING DOMAIN (e.g., bank.com.pk)
       |
       +---> DNSKEY (Zone Signing Key / Key Signing Key)
       +---> RRSIG  (Cryptographically Signed Resource Record Sets)
       +---> NSEC3  (Authenticated Denial of Existence)
Eliminating DNS Cache Poisoning and MitM Spoofing
Standard DNS queries transit cleartext UDP port 53. Unauthenticated recursive DNS resolvers are vulnerable to Kaminsky-style cache poisoning attacks, wherein an attacker floods an upstream resolver with forged DNS responses containing spoofed transaction IDs. Once poisoned, the resolver serves malicious IP addresses to thousands of downstream clients, seamlessly directing online banking customers, tax filers, and corporate VPN clients to phishing mirrors without raising browser transport alerts.
DNSSEC provides origin authentication and data integrity through asymmetric public-key cryptography:
- RRSIG (Resource Record Signature): Every DNS record set (A, AAAA, MX, CNAME) is cryptographically signed by the zone’s Zone Signing Key (ZSK).
- DNSKEY: Contains the public keys utilized by resolvers to verify the cryptographic signatures.
- DS (Delegation Signer): A cryptographic hash of the zone’s Key Signing Key (KSK) submitted to the parent zone (
.pk), establishing an unbroken cryptographic chain of trust originating from the ICANN root zone.
Compliance Mandates for Resolvers and Registrars
- PKNIC Automation: The national
.pkregistry has integrated automated DS record provisioning into its registrar management portal, enabling enterprise zone operators to push and rotate DNSSEC keys programmatically via standard EPP (Extensible Provisioning Protocol) interfaces. - Mandatory Resolver Validation: All broadband providers, cellular data carriers, and commercial DNS providers operating within Pakistan must enable DNSSEC validation (
dnssec-validation auto;) on all recursive caching nameservers. Queries yielding forged or tampered RRSIG signatures returnSERVFAIL, completely isolating end-users from compromised domain records.
4. Telecom Compliance Timelines: Pakistan’s Phased Enforcement Roadmap
To ensure zero service disruption across critical national infrastructure, PTA, in conjunction with the National Cyber Security Operations Center (NCSOC) and Pak-CERT, has structured the enforcement framework into three non-negotiable operational phases:
Phase 1: Tier-1 LDI & Mobile Operators (Deadline: March 31, 2026)
- Covered Entities: Pakistan Telecommunication Company Limited (PTCL), Transworld Associates (TWA), Cybernet, Nayatel, Wateen Telecom, StormFiber, and all CMOs (Jazz, Telenor Pakistan, Zong, Ufone).
- Deliverables:
- Complete 100% ROA generation for all allocated sovereign IPv4 and IPv6 address blocks via APNIC MyAPNIC portal.
- Deployment of redundant RPKI validators across dual data centers in Karachi and Islamabad.
- Strict enforcement of
Invalid Dropfiltering policies on all external transit, private bilateral peering, and PKIX exchange sessions.
Phase 2: Commercial Banks, FinTechs & Government Backbones (Deadline: June 30, 2026)
- Covered Entities: State Bank of Pakistan (SBP) regulated commercial banks, 1LINK switch, Raast national instant payment rails, digital retail banks, Federal Board of Revenue (FBR), and NADRA.
- Deliverables:
- Direct signing of proprietary ASN address spaces.
- Complete DNSSEC deployment across all financial portals, transaction processing APIs, and authoritative DNS zones.
- Elimination of single-homed BGP configurations vulnerable to transit path manipulation.
Phase 3: Regional ISPs, Enterprise Autonomous Systems & Educational Networks (Deadline: October 31, 2026)
- Covered Entities: Regional category ISPs, software technology parks, enterprise campus networks, and the Pakistan Education & Research Network (PERN).
- Deliverables:
- Full ROA registration covering all downstream customer allocations.
- Mandatory activation of DNSSEC validation on all local enterprise caching resolvers.
- Audit certification submission to the PTA Cyber Security Directorate.
Failure to comply with Phase deadlines triggers escalating regulatory sanctions under Section 23 of the Pakistan Telecommunication (Re-organization) Act, including administrative fines and operational suspension of transit peering permissions.
5. Architectural Comparison: Legacy BGP Routing vs. PTA RPKI-ROV Mandate
The structural leap from unauthenticated routing to RPKI ROV with DNSSEC validation fundamentally transforms the threat landscape across Pakistan’s internet exchanges:
| Operational Dimension | Legacy Unauthenticated Routing (Pre-2026) | PTA Mandated RPKI-ROV & DNSSEC (2026) |
|---|---|---|
| Route Authorization | Implicit trust based on raw BGP path announcements. | Explicit cryptographic proof signed by APNIC Trust Anchor. |
| Prefix Hijack Defense | Manual detection via looking glasses, alert emails, and delayed NOC intervention. | Automated, sub-second route dropping at the line card of border routers. |
| Sub-Prefix Leak Prevention | Highly vulnerable; more-specific advertisements (/24) bypass aggregate filters. |
Enforced MaxLength parameters automatically invalidate unauthorized sub-prefixes. |
| DNS Resolution Security | Unsigned cleartext UDP queries; vulnerable to cache poisoning and MitM injection. | Digitally signed RRSIG records validated against the root zone chain of trust. |
| Transit Hairpinning Risk | Domestic traffic frequently leaked onto overseas submarine transits. | Domestic traffic strictly confined within local PKIX fabrics and certified paths. |
| FinTech & Banking Impact | Severe vulnerability to counterfeit SSL/TLS certificates through routing detours. | Absolute cryptographic assurance of origin path and authentic IP destinations. |
6. Enterprise Infrastructure Imperative: Securing High-Availability Systems
The enforcement of RPKI and DNSSEC dramatically improves the security posture of the national backbone, but it also creates profound operational imperatives for enterprise engineering teams, digital banking architects, and mission-critical SaaS platforms.
In an automated ROV ecosystem, network routers unconditionally discard invalid routes. If an enterprise relies on fragmented, multi-tenant public cloud instances hosted offshore or shared hosting environments whose upstream transit providers fail to maintain rigorous ROA records, unexpected routing blackholes can isolate services from domestic users.
To achieve continuous availability, compliance, and deterministic packet delivery, enterprise applications, core transactional databases, and payment processors must anchor their production infrastructure on carrier-grade, RPKI-validated networks.
Sovereign Multihomed Dedicated Infrastructure
Deploying on enterprise-grade domestic infrastructure ensures that digital platforms operate within fully verified autonomous systems directly connected to domestic Tier-1 fiber rings and PKIX peering fabrics:
- Carrier-Neutral Multihomed Connectivity: Enterprise workloads hosted on Nextgen Dedicated Servers benefit from multi-carrier BGP failover across fully RPKI-compliant upstream Tier-1 providers. This architecture guarantees that traffic automatically routes around upstream carrier failures without triggering route invalidation or transit flapping.
- Low-Latency Domestic Edge Performance: Utilizing high-performance Dedicated Servers in Pakistan deployed across Tier-3 carrier-neutral facilities in Karachi and Islamabad confines domestic banking, commerce, and enterprise traffic entirely within local boundaries. This achieves deterministic round-trip times (RTT) under 5ms while eliminating cross-border transit loops and offshore surveillance vulnerabilities.
- Dedicated Cryptographic Assurance: Unlike shared hypervisors where neighboring virtual instances can compromise network stability, dedicated bare-metal hardware guarantees full control over network interface cards, hardware security modules (HSMs), local DNSSEC signing engines, and automated ROA renewal pipelines.
By aligning enterprise deployment architectures with PTA’s RPKI and DNSSEC framework, forward-thinking organizations can bulletproof their digital services against routing hijacks, achieve full regulatory compliance, and provide uninterrupted performance to millions of users across Pakistan.
Deploy BGP-Resilient Dedicated Servers in Pakistan
Protect your enterprise systems, banking APIs, and high-traffic applications from BGP prefix hijacks and routing anomalies. Nextgen Hosting delivers enterprise bare-metal dedicated servers and high-availability infrastructure housed in Tier-3 Karachi and Islamabad datacenters, directly peered with PKIX with full RPKI Route Origin Validation and sub-5ms domestic latency.
Related Technical Architecture & Infrastructure Analysis
- PTA Activates Domestic DDoS Scrubbing Centers in Karachi and Lahore – In-depth review of national volumetric DDoS mitigation pipelines.
- Pakistan 5G Standalone Architecture: C-Band Optimization and Edge Cloud – Technical engineering overview of 5G Standalone core and user plane functions.
- SBP and PTA Post-Quantum Cryptography Migration Mandate 2028 – Regulatory roadmap for quantum-resistant cryptographic algorithms across Pakistan.
- High-Performance Pakistan VPS Cloud Infrastructure – Scalable, locally hosted cloud virtual servers with direct domestic peering.