
Default SSH installations on newly deployed cloud servers are prime targets for automated malicious scanners. Within minutes of provisioning a public IP address in Pakistan, your /var/log/auth.log or secure logs will record thousands of brute-force attempts probing standard user accounts (root, admin, ubuntu, test). Leaving standard password authentication enabled on default port 22 is an open invitation to server hijacking, crypto-mining malware, and catastrophic data loss.
Securing SSH requires a defense-in-depth model: replacing legacy RSA keys with modern elliptic-curve Ed25519 cryptography, enforcing strict privilege separation, disabling password authentication entirely, masking the listening daemon, and layering multi-factor authentication (MFA/2FA) via Time-based One-Time Passwords (TOTP).
In this masterclass, we will walk through a production-grade SSH hardening blueprint for Ubuntu, Debian, AlmaLinux, and Rocky Linux on both Cloud VPS instances and enterprise Dedicated Servers.
1. Cryptographic Upgrade: Why Ed25519 Replaces RSA
For decades, RSA keys (2048 or 4096-bit) were the industry standard. However, modern cryptographic standards have shifted decisively toward Ed25519 (Edwards-curve Digital Signature Algorithm over Curve25519):
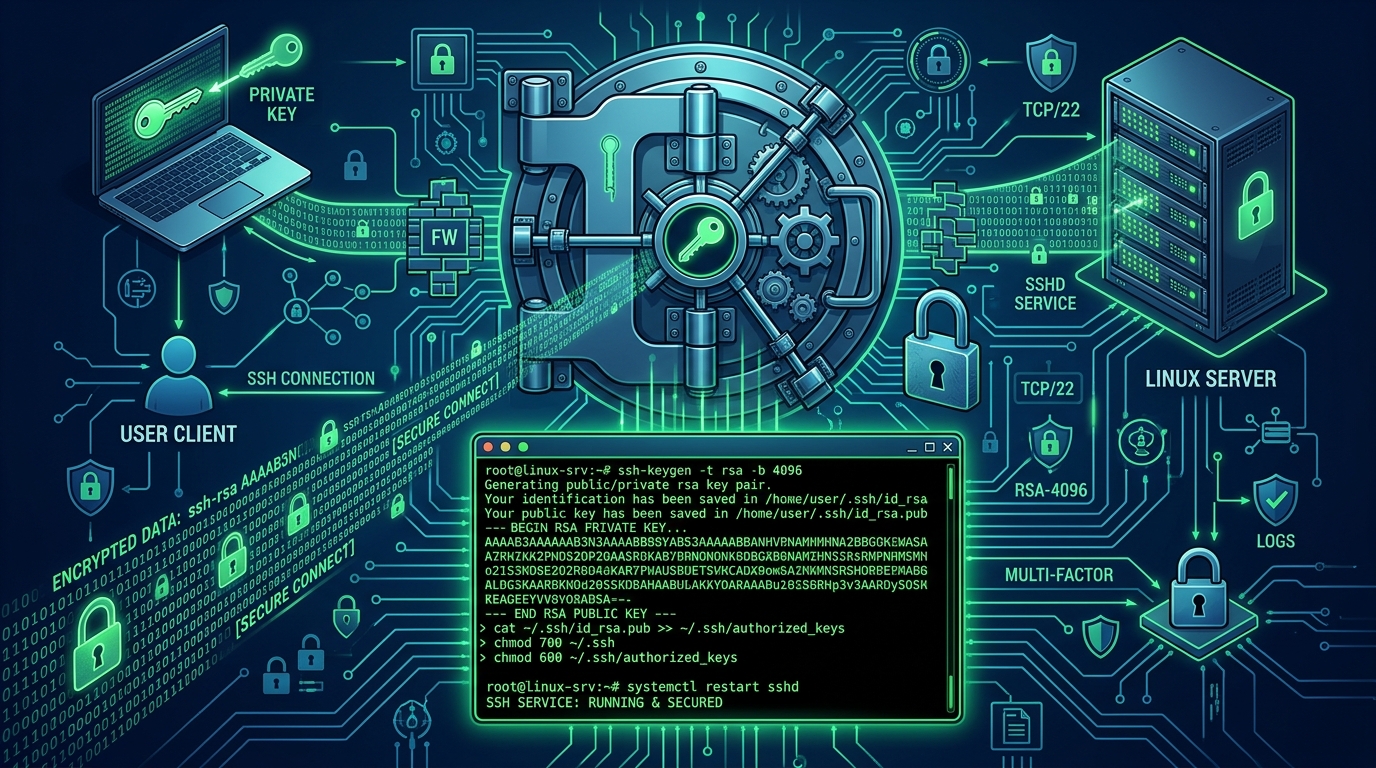
Generating an Ed25519 Key Pair
On your local workstation (macOS, Linux, or Windows PowerShell):
# Generate an Ed25519 key pair with 100 rounds of key derivation hashing
ssh-keygen -t ed25519 -a 100 -C "[email protected]"

# Push the public key to your remote Linux server
ssh-copy-id -i ~/.ssh/id_ed25519.pub -p 22 adminuser@your-server-ip
2. Hardening /etc/ssh/sshd_config: Production Blueprint
Connect to your server as a non-root administrative user with sudo privileges. Open /etc/ssh/sshd_config (or create a drop-in file at /etc/ssh/sshd_config.d/99-hardened.conf):
# /etc/ssh/sshd_config.d/99-hardened.conf

# 1. Network & Port Isolation
# Change default port 22 to a non-standard port (e.g. 2222 or 54222)
Port 54222
AddressFamily inet
ListenAddress 0.0.0.0

# 2. Authentication Restrictions
# Completely forbid root direct login
PermitRootLogin no

# Enforce public key authentication strictly
PubkeyAuthentication yes
PasswordAuthentication no
PermitEmptyPasswords no
AuthenticationMethods publickey

# Disable legacy and insecure authentication mechanisms
ChallengeResponseAuthentication no
KbdInteractiveAuthentication no
GSSAPIAuthentication no
KerberosAuthentication no

# 3. Connection & Session Hardening
# Terminate idle sessions after 10 minutes of inactivity
ClientAliveInterval 300
ClientAliveCountMax 2

# Limit concurrent unauthenticated connections (Anti-DoS)
MaxStartups 10:30:100
MaxAuthTries 3
LoginGraceTime 30

# 4. Modern Cryptographic Ciphers & MACs Only
KexAlgorithms curve25519-sha256,[email protected],diffie-hellman-group16-sha512,diffie-hellman-group18-sha512
Ciphers [email protected],[email protected]
MACs [email protected],[email protected]
Critical Safety Step: Test Configuration Before Restarting!
Never restart the SSH daemon without validating configuration syntax first:
sudo sshd -tIf this returns zero output, your syntax is valid.
Before closing your current terminal session, open your firewall for the new port and restart SSH:
# Allow new port through UFW (Ubuntu/Debian)
sudo ufw allow 54222/tcp

# Or allow through firewalld (AlmaLinux/Rocky Linux)
# sudo firewall-cmd --permanent --add-port=54222/tcp && sudo firewall-cmd --reload

# Restart SSH service
sudo systemctl restart sshd
Always open a second terminal tab to confirm successful connection on port 54222 before closing your current active session!
3. Implementing Multi-Factor Authentication (MFA / 2FA) via Google Authenticator
For defense-grade security, mandate that administrators provide both their private SSH key AND a time-sensitive 6-digit TOTP code generated on their mobile authenticator app.
Step 1: Install PAM Google Authenticator Module
# Ubuntu / Debian
sudo apt-get install -y libpam-google-authenticator

# AlmaLinux / Rocky Linux
sudo dnf install -y google-authenticator
Step 2: Initialize TOTP for the Administrative User
Run the setup wizard as your regular administrative user:
google-authenticator- Make tokens time-based: y
- Scan the displayed ASCII QR code with your mobile app (Google Authenticator, Bitwarden, or 1Password).
- Save the displayed emergency scratch codes in a secure offline vault!
- Disallow multiple uses of the same token: y
- Permit window skew tolerance: n
- Enable rate limiting (max 3 logins per 30s): y
Step 3: Configure PAM & SSH for Dual Authentication
Edit /etc/pam.d/sshd:
# Append to the bottom of /etc/pam.d/sshd:
auth required pam_google_authenticator.so nullok
Update /etc/ssh/sshd_config.d/99-hardened.conf to require both factors sequentially:
KbdInteractiveAuthentication yes
AuthenticationMethods publickey,keyboard-interactive
Restart SSH:
sudo systemctl restart sshdNow, when logging into the server, SSH first cryptographically verifies your Ed25519 private key, and immediately prompts:
Verification code: ______Even if an attacker gains possession of your workstation’s private key, they cannot access your server without the physical MFA device!
4. Pairing with Intrusion Prevention
Host-level SSH hardening should always be coupled with dynamic behavioral blocking to thwart automated scanners trying old usernames.
Explore our technical tutorials on:
- Fail2ban Custom Jails for SSH & cPanel Hardening
- Docker Firewall Hardening with iptables and UFW
- ModSecurity OWASP CRS Tuning & False Positive Suppression
For organizations managing sensitive customer data, payment gateways, and fintech platforms, deploying dedicated physical hardware isolates your infrastructure at the rack level. Explore our high-security Dedicated Servers in Pakistan.
Deploy Hardened Cloud VPS & Bare Metal in Pakistan
Protect your business assets with isolated networking, enterprise DDoS mitigation, and low-latency infrastructure across Karachi, Lahore, and Islamabad.
