
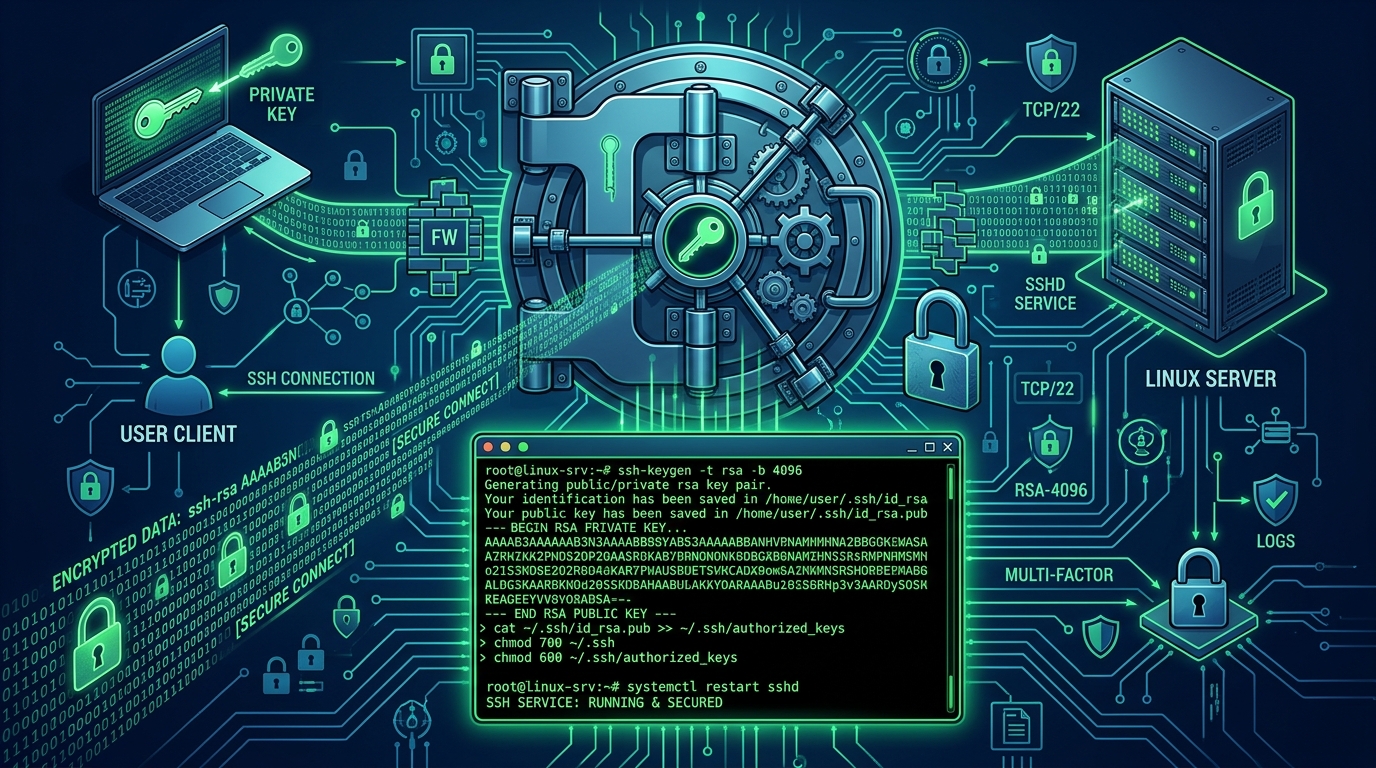
Every public-facing Linux server connected to the Internet receives thousands of automated connection attempts on port 22 every single day. Global botnets, credential scanners, and automated dictionary tools continually probe for weak passwords, leaked private keys, and default administrative usernames.
For systems engineers managing mission-critical databases, cPanel hosting environments, and microservices on Dedicated Servers in Pakistan, securing the Secure Shell (SSH) daemon is your first and most vital operational responsibility.
Relying on legacy RSA keys with password authentication enabled is an invitation to automated compromise.
In this comprehensive security guide, we explore how to transition to modern ED25519 elliptic-curve keys, configure aggressive automated IP banning using Fail2ban, and enforce strict cryptographic parameters across your Linux infrastructure.
Why ED25519 Replaces Legacy RSA Keys
For decades, RSA-2048 and RSA-4096 were the default public-key standards. However, modern cryptography has firmly shifted to ED25519 (Edwards-curve Digital Signature Algorithm over Curve25519):
Comparison: RSA-4096 vs ED25519
├── Key Size: RSA is 4096 bits (bloated); ED25519 is 256 bits (compact)
├── Generation Speed: ED25519 generates in <1ms; RSA takes seconds
├── Signature Verification: ED25519 is 3x to 5x faster (reduces server CPU overhead)
└── Side-Channel Resilience: ED25519 immune to cache-timing attacks
Step 1: Generating Modern ED25519 Keypairs
Generate an ED25519 key on your local client machine with a strong passphrase and 100 rounds of Key Derivation Function (KDF):
# Generate hardened ED25519 SSH keypair
ssh-keygen -t ed25519 -a 100 -C "[email protected]"
Copy the public key to your remote server:
ssh-copy-id -i ~/.ssh/id_ed25519.pub -p 22 [email protected]Verify that permissions on the remote server’s ~/.ssh directory are strictly locked down:
chmod 700 ~/.ssh
chmod 600 ~/.ssh/authorized_keys
Step 2: Hardening /etc/ssh/sshd_config
Open /etc/ssh/sshd_config or create a drop-in file at /etc/ssh/sshd_config.d/99-hardening.conf:
# 1. Move off default port 22 to eliminate automated scanner noise
Port 2222

# 2. Disable direct root login (force privilege escalation via sudo)
PermitRootLogin prohibit-password

# 3. Completely disable password authentication
PasswordAuthentication no
ChallengeResponseAuthentication no
PubkeyAuthentication yes

# 4. Enforce strict key and MAC algorithms (Mozilla Modern OpenSSH)
KexAlgorithms curve25519-sha256,[email protected],diffie-hellman-group16-sha512
Ciphers [email protected],[email protected]
MACs [email protected]

# 5. Restrict idle connection persistence
ClientAliveInterval 300
ClientAliveCountMax 2

# 6. Disable unsafe legacy forwarding
X11Forwarding no
AllowAgentForwarding no
Validate configuration syntax before reloading:
sudo sshd -t && sudo systemctl reload sshdStep 3: Installing and Tuning Fail2ban for Automated Defense
Fail2ban continuously monitors authentication logs (/var/log/auth.log on Debian/Ubuntu or /var/log/secure on RHEL/AlmaLinux). When an IP address exceeds the allowed threshold of failed attempts, Fail2ban dynamically injects an iptables or nftables drop rule.
1. Install Fail2ban:
# On Ubuntu / Debian
sudo apt update && sudo apt install fail2ban -y

# On AlmaLinux / Rocky Linux
sudo dnf install epel-release -y
sudo dnf install fail2ban fail2ban-systemd -y
2. Configure /etc/fail2ban/jail.local:
Create a custom configuration override file:
[DEFAULT]
# Whitelist local management IPs and office static addresses
ignoreip = 127.0.0.1/8 ::1 202.59.80.12 10.8.0.0/24

# Ban duration: 24 hours
bantime = 86400

# Evaluation window: 10 minutes
findtime = 600

# Max retries before ban
maxretry = 3

# Netfilter backend (auto detects nftables / iptables)
banaction = iptables-multiport

[sshd]
enabled = true
port = 2222
logpath = %(sshd_log)s
backend = systemd
Enable and start the service:
sudo systemctl enable --now fail2ban3. Inspecting Active Jail Status:
Verify that Fail2ban is monitoring your custom SSH port:
sudo fail2ban-client status sshdSample output:
Status for the jail: sshd
|- Filter
|  |- Currently failed: 1
|  |- Total failed:     42
`- Actions
   |- Currently banned: 3
   |- Total banned:     14
   `- Banned IP list:   185.220.101.5 45.154.255.12 194.26.29.8
Step 4: Defense-in-Depth on Enterprise Bare Metal
For mission-critical production fleets on Dedicated Servers, add an additional layer of security:
- TCP Wrappers (
/etc/hosts.allow): Restrict SSH connection handshakes to specific internal VPN subnets. - Port Knocking or Single Packet Authorization (fwknop): Keep your SSH port completely closed to all public port scans until a cryptographically signed UDP knock packet unlocks it.
With ED25519 keys enforced, password logins barred, and Fail2ban scanning the perimeter, your Linux infrastructure remains resilient against automated intrusion attempts.
Deploy Pre-Hardened Linux Dedicated Servers in Pakistan
Protect your critical databases and application fleets with enterprise bare-metal hosting. NextGen Dedicated Servers feature hardware DDoS mitigation, isolated out-of-band IPMI, pure NVMe arrays, and 24/7 priority support.
