
Automated bot traffic now accounts for more than 48% of all internet requests. For online businesses, e-commerce stores, and digital publishers in Pakistan, malicious bots pose three existential threats:
- Aggressive Content & Price Scraping: Competitors deploy automated Python scrapers to steal product catalogs and undercut prices in real time.
- Credential Stuffing & Brute Force: Cybercriminals bombard WordPress
wp-login.phpand WooCommerce checkout endpoints with leaked password dumps. - Severe Origin Resource Exhaustion: Thousands of concurrent bot requests bypass application caches, spiking origin server CPU to 100% and causing legitimate human visitors to experience
504 Gateway Timeouterrors.
To combat this at the edge, Cloudflare offers Super Bot Fight Mode (SBFM) and Cloudflare Bot Management (BM). This in-depth guide explains how these machine-learning systems function, how to configure them properly, and how to avoid blocking critical Pakistani payment gateway webhooks.
Executive Summary: Cloudflare Bot Defense Tiers
- Free Bot Fight Mode: Binary protection that issues JavaScript challenges to suspected bots. Cannot be customized, and often blocks legitimate API webhooks.
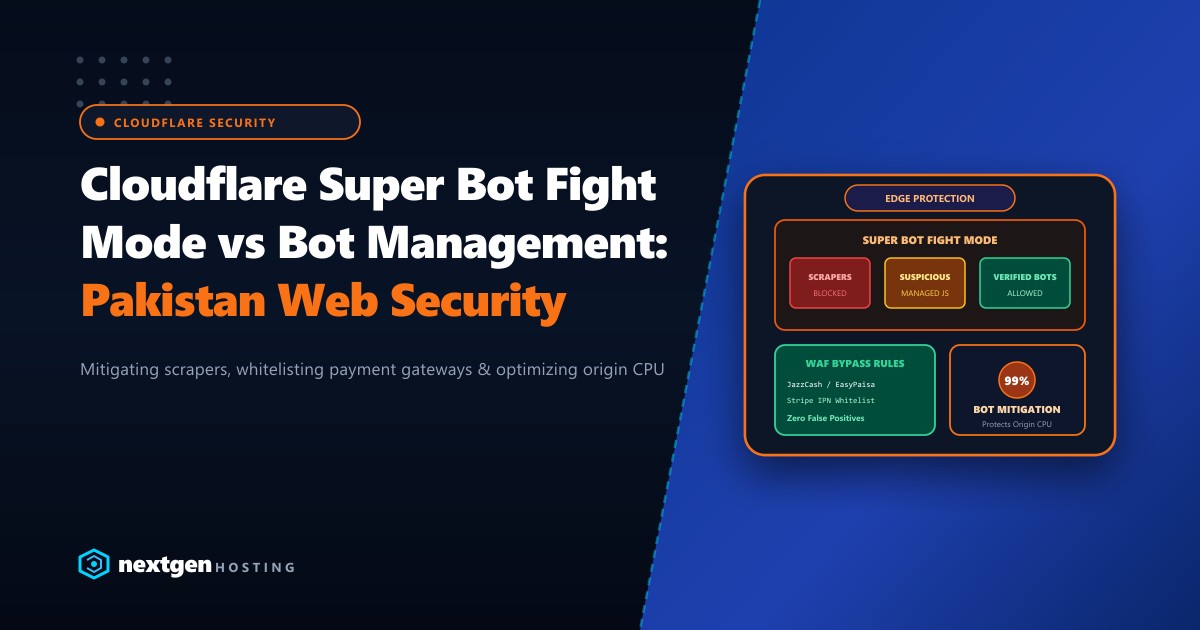
- Super Bot Fight Mode (Pro & Business): Granular controls allowing administrators to differentiate between Definitely Automated, Likely Automated, and Verified Bots with options to Block, Challenge, or Allow.
- Enterprise Bot Management: Assigns dynamic Machine Learning Bot Scores (1–99) to every incoming request, enabling deep custom WAF expression rules.
- Webhook Whitelisting Criticality: In Pakistan, failing to configure bypass rules for JazzCash, EasyPaisa, or PayFast IPN webhooks will cause payment confirmations to fail silently under Super Bot Fight Mode.
Understanding Cloudflare’s Bot Detection Architecture
Cloudflare analyzes over 55 million HTTP requests per second across its global Anycast edge network. Rather than relying on simple User-Agent strings (which can be easily forged by attackers), Cloudflare evaluates client behavior using heuristic fingerprints:
Incoming Request -> Anycast Edge Node
                          |
             [ Heuristic Analysis Engine ]
   - TLS Client Fingerprint (JA3 / JA4)
   - HTTP/2 & HTTP/3 Frame Serialization
   - TCP Packet Window Parameters
   - Behavioral Request Cadence (Frequency)
                          |
     +--------------------+--------------------+
     |                                         |
[ Verified Search Engine Bot ]     [ Suspicious / Automated Client ]
(Googlebot, Bingbot, Yandex)                   |
     |                                    Bot Score: 1 - 29
   ALLOW                                       |
                         +---------------------+---------------------+
                         |                                           |
               [ Action: BLOCK ]                          [ Action: MANAGED CHALLENGE ]
             (Headless Puppeteer/cURL)                     (Interactive Turnstile Test)
The Three Traffic Classifications
- Verified Bots: Good bots that follow robots.txt protocols and publish official IP ranges (e.g., Googlebot, Bingbot, Pingdom uptime monitors). These are allowed by default.
- Definitely Automated: Traffic generated by automated tools like Scrapy, cURL, Selenium, or headless Chromium instances that exhibit clear automated signatures.
- Likely Automated: Clients exhibiting anomalous behavior (e.g., browsing hundreds of product pages per second from residential proxy subnets) that warrant a cryptographic challenge.
Configuring Super Bot Fight Mode (Pro & Business Tiers)
To configure Super Bot Fight Mode for optimal protection without disrupting legitimate traffic:
- Log in to the Cloudflare Dashboard and select your domain.
- In the left navigation, navigate to Security >> Bots.
- Click Configure Super Bot Fight Mode.
Recommended Production Configuration:
| Traffic Category | Recommended Action | Technical Rationale |
|---|---|---|
| Definitely Automated | Block or Managed Challenge | Instantly stops basic scrapers and brute-force credential stuffing without touching origin servers. |
| Likely Automated | Managed Challenge | Delivers an invisible, frictionless Cloudflare Turnstile verification. Human users pass instantly; automated headless bots fail. |
| Verified Bots | Allow | Essential to prevent accidental de-indexing of your website from Google and Bing search results. |
| Static Resource Protection | Off | Keep this toggle disabled unless your site suffers from image or PDF bandwidth hotlinking. |
The Critical Pakistan Pitfall: Whitelisting Local Payment Gateways
When Pakistani e-commerce stores activate Super Bot Fight Mode, a common crisis occurs: customer orders remain in “Pending Payment” status even though funds were deducted from their bank accounts.
Why This Happens
Local payment gateways (such as JazzCash, EasyPaisa, PayFast, Kuickpay, and Bank Alfalah) send server-to-server Instant Payment Notifications (IPNs) via HTTP POST webhooks to your server (e.g., https://yourstore.pk/wc-api/WC_Gateway_Jazzcash).
Because these webhooks originate from automated financial server scripts without a human browser session, Cloudflare’s bot engine flags them as “Definitely Automated” and blocks or challenges them. Since automated scripts cannot solve a JavaScript challenge, the webhook fails.
The Fix: Creating WAF Skip Rules for Payment Endpoints
To prevent this, navigate to Security >> WAF >> Custom Rules and create an exception rule that precedes Bot Fight Mode:
Rule Name: Whitelist Payment Webhooks & IPNs
If incoming requests match:
  (http.request.uri.path contains "/wc-api/") or
  (http.request.uri.path contains "/payment-callback/") or
  (ip.src in {175.107.0.0/16 202.163.0.0/16}) # Replace with actual gateway IP blocks

Then:
  Choose Action: Skip
  WAF components to skip:
    ☑ Super Bot Fight Mode
    ☑ Security Level
    ☑ Browser Integrity Check
[ JazzCash / EasyPaisa Server ] -> HTTP POST Webhook
|
[ Cloudflare Edge ]
|
Matches WAF Skip Rule?
/ \
[ YES ] [ NO ]
/ \
Bypasses Bot Challenge Triggers SBFM Challenge
/ \
Delivered to Origin Server (200 OK) Dropped / Blocked (403)Protecting Origin Infrastructure with Enterprise Hardware
While Cloudflare provides edge protection, sophisticated bots utilizing distributed residential proxies can sometimes spoof browser headers and hit your origin server.
To guarantee that your application remains immune to origin resource exhaustion, hosting on robust, isolated infrastructure is paramount. High-concurrency platforms benefit tremendously from enterprise Dedicated Servers featuring multi-core AMD EPYC processors and dedicated PCIe Gen4 NVMe arrays.
Furthermore, hosting Pakistani platforms on domestic Dedicated Servers in Pakistan ensures that legitimate domestic shoppers experience lightning-fast sub-10ms response times while international scraping bots are filtered out thousands of miles away at the Anycast edge.
Measuring Impact: Bot Analytics & Origin Offload
Within 48 hours of activating properly tuned bot defense, websites routinely observe:
- Origin CPU Utilization: Drops from 85% to under 20%.
- MySQL Processlist: Eliminates hundreds of concurrent slow queries caused by rapid pagination scraping.
- Bandwidth Savings: Reduces unmetered egress bandwidth by 30% to 50%.
- Security Logs: Clean, transparent audit logs of blocked malicious attacks available under Security >> Events.
Secure Your High-Traffic Platform with Nextgen
Combine enterprise Cloudflare edge security with raw bare-metal server performance. Protect your transactions, speed up TTFB, and defend against malicious scrapers with Nextgen Hosting.
